
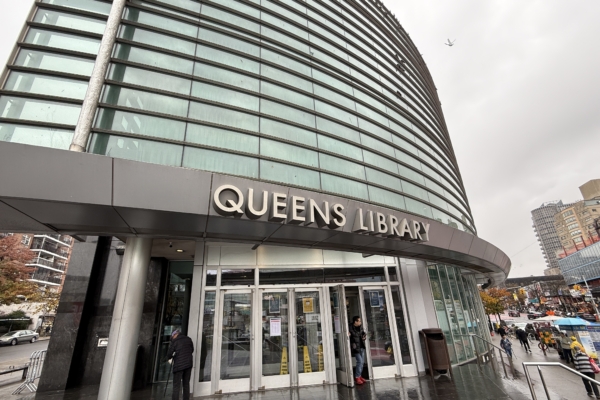
On November 4, the Queens Public Library (QPL) fell victim to a ransomware attack that caused a complete disruption of network services across its 66 branches. In the wake of this incident, library staff have worked diligently to restore some services gradually.
By Friday, November 6, updates from the Flushing branch indicated that the library’s Wi-Fi was back up and running, along with the self-checkout machines. However, it’s worth noting that borrowing limits were imposed for the time being, with patrons allowed to check out only five books at a time. Meanwhile, the return service has also been reinstated, enabling readers to return their borrowed items.
Despite these advances, critical digital resources remain unavailable. The library’s mobile application, website, and other digital media services like computer access and e-books are still offline, meaning that readers are currently unable to access any of these online resources.
The ransomware attack initially occurred on Wednesday, November 4, prompting a severe disruption of several services, including the library’s website, in-branch computers, self-checkout kiosks, free Wi-Fi, mobile applications, and digital media services. Despite the technological setbacks, all branches of the Queens Public Library continued to operate physically.
Dennis Walcott, the president and CEO of the Queens Public Library, disclosed that the library is working closely with the New York City Police Department (NYPD) and the Federal Bureau of Investigation (FBI) to investigate the ransomware incident and to ensure system recovery.
At this point, the identities of the hackers and their motives remain unclear, as does whether any personal data of library users has been compromised. The library has not revealed if the hackers issued specific ransom demands or the amount of money involved.
Walcott emphasized the unfortunate reality that cyberattacks are a pressing issue in today’s society, affecting not solely large corporations but also public institutions like libraries.
Previously, the library had informed the public that during the system failures, patrons could still visit branches to perform borrowing and returning duties, though the option to renew items momentarily was unavailable. Importantly, any items returned late due to the system disruption would not incur overdue fines.
As restoration of services progresses, the library’s network systems continue to undergo repair, and a timeline for full restoration of services remains uncertain. The situation is evolving, and staff are working tirelessly to mitigate the impact of this cyber incident on the community.